Aicot – Explained AI Cybersecurity for Critical Infrastructure!
If you searched for AICOT, you may have found several completely different technologies using the same acronym.
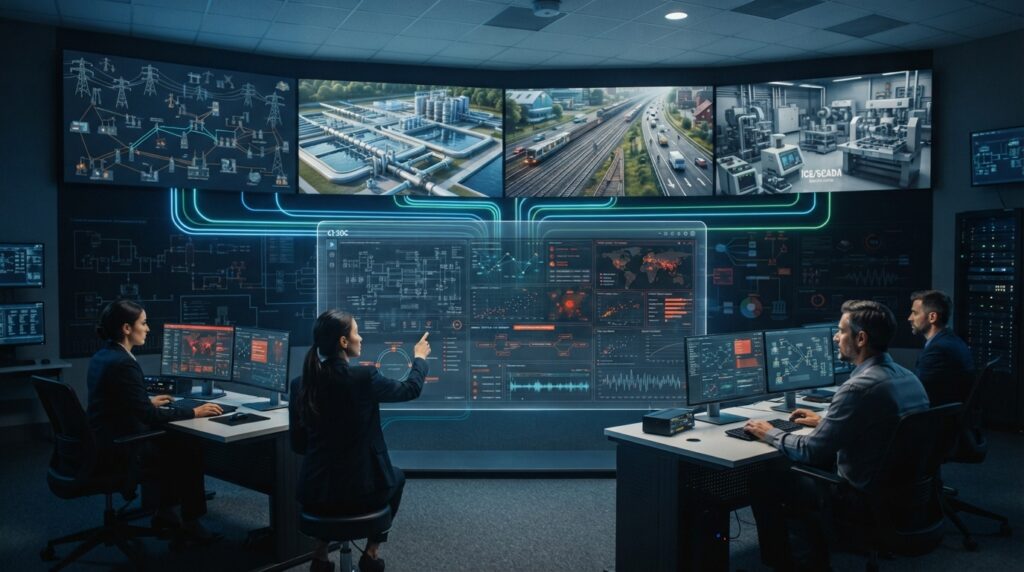
In the context of aicotproject.eu, AICOT refers to a European cybersecurity project focused on protecting Operational Technology (OT) environments used by critical infrastructure.
The project is developing an AI-driven cyber defense platform intended to monitor industrial environments, identify suspicious behavior, analyze OT-specific activity, use threat intelligence, and support faster cybersecurity response.
AICOT is therefore not simply another general-purpose AI tool. Its focus is the much more specialized problem of securing digital systems that interact with physical infrastructure.
What Is AICOT?
AICOT is an EU-funded project focused on AI-driven cybersecurity for Operational Technology in critical infrastructure.
Operational Technology includes the systems used to monitor or control physical processes. Depending on the industry, that can involve industrial controllers, sensors, machinery, pumps, turbines, production equipment, transportation systems, and other connected operational assets.
AICOT’s goal is to build an OT-native cybersecurity platform rather than applying ordinary IT security assumptions to industrial environments.
The project combines several technologies, including:
- Machine learning
- Anomaly detection
- SIEM and security analytics
- OT protocol analysis
- Cyber threat intelligence
- AI-assisted detection
- Secure information sharing
- Blockchain-based CTI infrastructure
The project is being coordinated by Logstail, which the official consortium page identifies as the single-member consortium lead.
What Problem Is AICOT Trying to Solve?
Modern industrial environments are increasingly connected.
An industrial network may communicate with corporate IT systems, remote-access platforms, cloud services, vendors, engineering workstations, monitoring systems, and other external components.
That connectivity can improve efficiency, but it also creates additional pathways for cyber threats.
The problem is particularly difficult because many OT environments were not designed around today’s cybersecurity assumptions.
Industrial systems may have:
- Legacy equipment
- Long operational lifetimes
- Specialized protocols
- Strict uptime requirements
- Vendor-specific configurations
- Safety considerations
- Limited tolerance for disruptive security controls
A security technique that works well on an ordinary office network may therefore be unsuitable for a production plant or other safety-sensitive environment.
AICOT is designed around that difference.
Why OT Security Is Different From IT Security
The most important concept to understand about AICOT is that OT is not simply another name for IT.
Information Technology generally focuses on computers, servers, applications, identities, data, and business networks.
Operational Technology is more closely connected to physical processes.
An IT security incident might compromise an employee account or business server.
An OT incident can potentially affect:
- Production
- Industrial machinery
- Energy delivery
- Water operations
- Transportation
- Physical processes
- Safety-critical systems
This changes the priorities.
An OT security team has to consider not only confidentiality and data protection, but also availability, process integrity, operational safety, and the potential physical consequences of an incident.
How Does AI Fit Into AICOT?
AICOT is designed to use artificial intelligence as part of its detection and analysis capabilities.
The basic idea is to identify behavior that differs from what would normally be expected in an industrial environment.
For example, a security system could potentially encounter:
- An unusual device communicating with another asset
- An unexpected command
- An abnormal network pattern
- A rare protocol interaction
- A change in normal industrial traffic
- Suspicious activity across several connected systems
A single event may not look dangerous by itself.
The challenge is determining whether several seemingly minor events form a meaningful pattern.
AI and machine-learning techniques can help analyze large quantities of telemetry and identify relationships that may be difficult to detect using simple fixed rules.
However, AICOT’s public project material describes these capabilities as development objectives. They should not be interpreted as proof that the completed platform already detects every type of attack or eliminates false positives.
What Is Anomaly Detection in AICOT?
Anomaly detection is the process of identifying activity that differs from an established pattern of normal behavior.
Imagine an industrial device that normally communicates with a small group of systems during specific operating periods.
If that device suddenly begins communicating with an unfamiliar system or issuing an unusual command, the event may deserve investigation.
An anomaly does not automatically mean an attack.
Maintenance, configuration changes, software updates, or legitimate operational events can also create unusual behavior.
The value of anomaly detection therefore depends on context.
AICOT’s goal is to make that context more useful by combining OT-specific information with cybersecurity data and analysis.
What Role Does SIEM Play?
SIEM stands for Security Information and Event Management.
A SIEM system collects and analyzes security-related information from multiple sources.
For an industrial environment, this might include:
- Security logs
- Network activity
- Authentication events
- Device information
- Alerts
- System events
- Other security telemetry
AICOT is being built on Logstail’s existing SIEM and data-analytics capabilities.
The project aims to add OT-specific intelligence so security teams can understand industrial activity in context rather than treating every event like a conventional IT security alert.
This is particularly important in environments where a large amount of normal machine-to-machine communication happens continuously.
What Is OT Protocol Analysis?
Industrial environments often use specialized communication protocols.
AICOT’s project material specifically references protocols including:
- Modbus
- DNP3
- PROFINET
- IEC 61850
These protocols are used in different industrial and infrastructure environments.
Understanding their traffic can help security systems interpret what is happening inside an OT network.
For example, a generic network monitoring tool may recognize that data is moving between two devices.
An OT-aware system aims to understand more about what that communication means in the industrial process.
That context can make security analysis more useful.
Which Industries Could AICOT Support?
AICOT is focused on critical infrastructure and other environments that rely heavily on Operational Technology.
The project’s materials highlight areas including:
Energy
Energy infrastructure depends on industrial control systems and networks that must remain available and reliable.
Cybersecurity incidents in these environments can have consequences beyond the organization’s internal network.
Water
Water and wastewater systems use OT to monitor and control physical processes.
Protecting these systems requires security measures that account for operational continuity.
Transport
Transportation infrastructure increasingly depends on connected digital systems.
OT security can therefore become part of the broader resilience strategy for transportation environments.
Manufacturing
Factories contain large numbers of connected machines, controllers, sensors, engineering systems, and industrial networks.
A cyber incident can potentially affect production as well as digital information.
What Is Cyber Threat Intelligence Sharing?
Cyber Threat Intelligence, often shortened to CTI, involves information about threats, attackers, indicators, techniques, vulnerabilities, and suspicious activity.
Sharing useful intelligence can help organizations recognize threats more quickly.
The problem is that industrial organizations may be reluctant to share sensitive information.
Their data can reveal:
- Network architecture
- Security weaknesses
- Industrial assets
- Incident details
- Operational information
AICOT’s project objectives include developing a secure and privacy-preserving approach to CTI exchange.
The project describes blockchain-backed infrastructure as part of that approach.
The intended benefit is not simply “putting cybersecurity on a blockchain.”
The larger objective is to create a trusted mechanism for exchanging useful threat intelligence without unnecessarily exposing sensitive operational information.
Why Does European Digital Sovereignty Matter?
AICOT also has a European strategic dimension.
Critical infrastructure operators depend on technology supply chains that can extend across multiple countries and vendors.
The AICOT project connects its cybersecurity objectives with European digital sovereignty, meaning greater European capability and control over technologies considered strategically important.
The idea is not necessarily to eliminate every non-European technology.
Instead, it is about strengthening Europe’s ability to develop, deploy, and maintain important cybersecurity capabilities within a trusted technological ecosystem.
This is consistent with the wider European policy focus on strengthening AI capability, cybersecurity resilience, strategic technology capacity, and digital autonomy.
Who Is Behind AICOT?
The official AICOT consortium page identifies Logstail as the single-member consortium leading the project.
According to the project information, Logstail’s responsibilities include:
- Overall project coordination
- Design and development of the AI-powered OT cybersecurity platform
- AI research and evaluation
- Secure CTI exchange infrastructure
- Pilot preparation and validation
- Dissemination and communication
This makes Logstail the central organization to follow for project developments.
Is AICOT Funded by the European Union?
Yes.
The official AICOT website states that the project receives funding through the European Union’s Digital Europe Programme.
The project lists grant agreement 101249826.
The official website also includes the standard disclaimer that project views and opinions belong to the authors and do not necessarily represent the European Union or the European Cybersecurity Competence Centre.
That funding information is useful when distinguishing the AICOT project from unrelated uses of the AICOT name.
Is AICOT a Finished Commercial Product?
This is an important distinction.
AICOT should currently be understood as a project developing and validating a cybersecurity platform, not simply assumed to be a fully mature commercial product available to every organization.
The project’s public objectives include pilot deployment and validation in realistic OT scenarios.
Its target is described as Technology Readiness Level 7–8.
That indicates an emphasis on moving the technology toward realistic operational validation.
It does not automatically mean that every planned capability is already available, commercially deployed, independently validated, or suitable for every industrial environment.
For current availability, deployment options, pilot opportunities, and project milestones, the official AICOT and Logstail channels should be checked.
What Does TRL 7–8 Mean for AICOT?
TRL stands for Technology Readiness Level.
It is a framework used to describe how mature a technology is.
In simple terms, the AICOT project’s TRL 7–8 objective indicates an intention to validate the technology in realistic or operationally relevant environments rather than leaving it only at the laboratory-concept stage.
That distinction is important.
A cybersecurity prototype can perform well in a controlled demonstration but face very different challenges when connected to a real industrial environment.
Real-world validation helps test:
- Scalability
- Reliability
- Usability
- Integration
- Detection quality
- Operational impact
- Deployment constraints
What Challenges Does AICOT Face?
AI does not automatically solve OT cybersecurity.
Several difficult problems remain.
False positives
Industrial networks can generate large amounts of legitimate unusual activity.
An AI system needs to distinguish genuine threats from normal operational changes.
Limited training data
High-quality labeled OT attack data can be difficult to obtain.
Industrial organizations cannot simply generate unlimited attack scenarios on live infrastructure.
AICOT therefore identifies domain-specific data and synthetic or adversarial samples as important challenges.
Legacy systems
Many industrial environments contain equipment that is old, specialized, or difficult to replace.
Security technology has to work around those constraints.
Integration
Organizations rarely operate one isolated security product.
A new platform must work alongside existing monitoring, networking, asset-management, security operations, and industrial systems.
Safety
In a critical infrastructure environment, an incorrect automated response can create its own risk.
For that reason, cybersecurity automation must be designed carefully around the operational environment.
AICOT vs Other Uses of the Name
The acronym AICOT is not unique.
This matters when researching the project.
For example, OMRON uses AICOT to refer to Anti-Islanding Control Technology, a technology related to solar power systems and grid-connected photovoltaic installations.
Other websites also use “Aicot” for unrelated AI consulting or technology concepts.
Therefore, a page about the AICOT cybersecurity project should ideally include the domain or the phrase AICOT Project when context matters.
If you are researching the project discussed in this article, aicotproject.eu is the relevant entity.
Why AICOT Matters for OT Cybersecurity
The larger significance of AICOT is the problem it is attempting to address.
Industrial systems are becoming increasingly connected, while many OT environments still depend on legacy equipment and specialized protocols.
That combination creates a difficult security environment.
A useful OT defense platform needs to understand more than IP addresses and conventional security alerts.
It needs operational context.
That is where AICOT’s combination of AI, anomaly detection, OT protocol analysis, SIEM data, and threat intelligence becomes relevant.
The project’s success will ultimately depend on how well those components work together in realistic industrial environments.
Frequently Asked Questions
1. What is AICOT?
In the context of the AICOT Project website, AICOT is an EU-funded project developing an AI-driven cybersecurity platform for Operational Technology environments in critical infrastructure.
2. What does AICOT stand for?
The project website primarily uses AICOT as the project name and describes it as an AI-driven cyber defense platform for OT. It does not prominently provide a conventional letter-by-letter expansion of the acronym, so inventing one would be misleading.
3. Who is developing AICOT?
The official consortium page identifies Logstail as the single-member consortium leading AICOT.
4. Who funds the AICOT project?
AICOT receives funding through the European Union’s Digital Europe Programme under grant agreement 101249826.
5. What is AICOT used for?
The project is intended to support cybersecurity monitoring, detection, analysis, and response for OT environments used in critical infrastructure.
6. Does AICOT use artificial intelligence?
Yes. AI and machine learning are central to the project’s planned approach, including anomaly detection and proactive detection of stealthy or previously unseen threats.
7. Which industries does AICOT target?
The project identifies OT environments in sectors such as energy, transport, water, and manufacturing.
8. What industrial protocols does AICOT consider?
The official project material references Modbus, DNP3, PROFINET, and IEC 61850 among the OT protocols relevant to its work.
9. Is AICOT available to buy?
The public project material reviewed presents AICOT primarily as a project under development and validation rather than a conventional off-the-shelf consumer product. Current commercial or pilot availability should be verified through the official project channels.
10. Is AICOT the same as OMRON AICOT?
No. They are different entities that happen to use the same acronym. OMRON’s AICOT refers to Anti-Islanding Control Technology, while the AICOT Project discussed here concerns AI-driven OT cybersecurity.
11. Is AICOT a replacement for a SIEM?
Not necessarily. The project is being developed on top of existing SIEM and data-analytics capabilities, with additional OT-specific analysis and AI-driven capabilities.
Final Verdict
AICOT is an EU-funded cybersecurity project focused on using AI and OT-specific security technology to improve protection of critical infrastructure. Its approach combines machine learning, anomaly detection, SIEM capabilities, OT protocol analysis, threat intelligence, and secure information sharing.
The project is particularly relevant because traditional IT security assumptions do not always fit industrial environments. OT systems can involve legacy equipment, specialized protocols, strict uptime requirements, and physical consequences when digital systems are compromised.
AICOT is being developed and validated rather than being treated as a universal, finished cybersecurity solution. Its planned pilot deployments and TRL 7–8 target will be important indicators of how successfully the technology moves from project development toward realistic operational use. For anyone researching the name AICOT, the most important first step is to identify the correct entity. In this case, AICOT Project at aicotproject.eu refers to AI-driven cybersecurity for Operational Technology and critical infrastructure, led by Logstail and supported through the EU Digital Europe Programme.